Atlaslive’s 2025 Summer Brief: Phishing Continues to Top the Cyber Threat List
Tuesday 16 de September 2025 / 12:00
⏱ 3 min read
(Lisbon).- Phishing continues to dominate the cybersecurity threat landscape in 2025, reaffirming its position as the most prevalent attack vector. According to APWG, the first quarter alone saw over 1 million phishing incidents—marking the highest surge since the end of 2023. Compared to last year, weekly phishing attempts have skyrocketed by 180%, and the use of phishing emails to distribute infostealers increased by 84% throughout 2024.
Phishing has once again confirmed its status as the top cyber threat in 2025. In the first quarter alone, the APWG reported 1,003,924 phishing attacks, the highest figure since late 2023. Compared with 2023, weekly phishing activity has climbed 180%, while the delivery of infostealers via phishing emails rose 84% in 2024.
The conclusion is straightforward: phishing is no longer background noise. It’s a direct channel for credential theft, account takeovers, and business disruption. Atlaslive’s Information Security Lead, Maksym Shapoval, explains why phishing is so effective and how businesses can reduce the risks.
Phishing in 2025: A Persistent Danger
Phishing succeeds because it’s simple. Attackers impersonate trusted organizations to trick users into revealing passwords, payment data, or other sensitive information. These attacks no longer rely only on email—they also arrive via SMS (“smishing”) and phone calls (“vishing”), often with messages that look nearly identical to real corporate communications.
Major Incidents This Summer
Several high-profile cases highlight phishing’s reach in 2025:
● Google — A phishing chain through Salesforce CRM led to exposed data.
● Cisco — Victimized by vishing that granted attackers access to client records.
● Booking — Targeted in campaigns that have persisted since 2024.
● UK Tax Authority — A large-scale phishing scheme stole £47 million from 100,000 individuals.
These examples make it clear: phishing is a universal entry point for cybercrime, no matter the sector.
iGaming in the Spotlight
The iGaming industry, already heavily regulated, suffered a major breach in July 2025. One of the largest global betting operators confirmed that 800,000 user records were exposed, including IP addresses, emails, and user activity logs.
“The incident underscores why iGaming platforms are prime targets,” says Maksym Shapoval, Information Security Lead at Atlaslive. “They operate entirely online, process constant financial transactions, and handle vast volumes of personal data. The risks of social engineering attacks in this industry are significant.”
Even if payment information wasn’t stolen, personal data of this scale can be weaponized in follow-up attacks.
Atlaslive’s Recommendations: Defending Against Phishing
Because phishing exploits people as much as technology, protection requires several layers:
● Authentication & Access — Enforce 2FA, apply least privilege, segment networks, require dual approvals, and audit regularly.
● Email Security — Implement DMARC, DKIM, and SPF; monitor similar-looking domains; label external emails.
● Endpoint Protection — Use MDM/EDR solutions and monitor browsing activity.
● Preparedness — Centralize reporting, create response playbooks, alert staff quickly, and block malicious domains.
● Training — Run awareness programs and phishing simulations to encourage fast reporting.
● Governance — Make phishing defense part of ongoing policy and continuous review.
A consistent, layered approach reduces both the success rate of phishing attempts and their potential impact.
Conclusion
Summer 2025 confirmed that phishing remains the main starting point for serious cyber incidents — from tech companies to government organizations and iGaming platforms. These attacks are more refined and damaging than ever.
For businesses handling financial operations and sensitive data, ignoring phishing is no longer an option. Companies must embed multi-factor authentication, email protection, staff training, and structured response plans into their daily operations. Those who act now will be best prepared to protect customers, reputations, and long-term business growth.
Categoría:Reports
Tags: atlaslive,
País: Portugal
Región: EMEA

Event
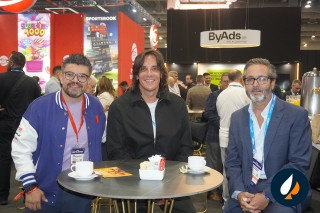
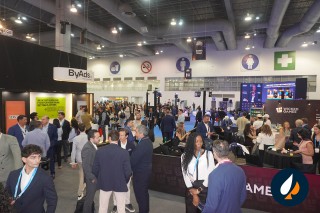
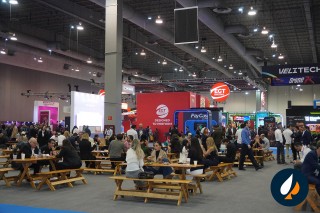
SiGMA North America 2026
01 de September 2026
LatAm Regulators Discussed Illegal Gambling and Innovation at SiGMA North America
(Mexico City, SoloAzar Exclusive).- The panel "The Red Pen Forum: Regulators Respond to the Industry," held during SiGMA North America 2026, brought together representatives from Uruguay, Argentina, Puerto Rico, and Honduras to analyze regulatory challenges, digital transformation, illegal gambling, and the need to adapt lotteries for new generations. The conference was moderated by Rodrigo Cigliutti, Executive Director of CIBELAE (Ibero-American Corporation of State Lotteries and Betting), and featured the participation of Marcelo Visconti, National Director of Lotteries and Quinielas of Uruguay; Carlos Moyano, President of IAFAS Entre Ríos, Argentina; Heidi Hernández Olivo, Deputy Secretary of the Puerto Rico Lottery; and Lissa Mencía, General Director of Lottery Operations and Games at Loto Honduras.
Monday 28 Sep 2026 / 12:00
SiGMA North America Addressed Crisis Management in iGaming
(Mexico, SoloAzar Exclusive).- During SiGMA North America 2026, Rosa Ochoa, founder of the Blue Global Gaming platform and strategic advisor for gaming operators; Iliana María Pineda Echeverri, Chief Legal & Compliance Officer at Wplay.co; Iraid Rosales, Country Manager Mexico at Amusnet; and Elizabeth Maya Cano, Executive President of CORNAZAR, analyzed the key factors in managing crisis situations within the iGaming industry, with a special focus on transparency, communication, technology, and preparation.
Friday 25 Sep 2026 / 12:00
Affiliates and Acquisition: Keys to Regulated Markets in North America
(Mexico City, SoloAzar Exclusive).- During SiGMA North America 2026, Cristopher Guzmán Reyes, Head of Affiliates at Logrand Entertainment Group; Guga Júnior, influencer and slots expert at Scalar Partners; Andrés Gómez, Head of Latin America Go-to-Market Strategy at Admattic; Yambot Aguilera, Gaming and Finance Sales Director at Google; and Paula Gabriel Jiménez, Advertising Client Growth Director for Microsoft at Aleph, analyzed the state and provincial affiliate ecosystem in North America, as well as the acquisition challenges in regulated markets.
Thursday 24 Sep 2026 / 12:00
SUSCRIBIRSE
Para suscribirse a nuestro newsletter, complete sus datos
Reciba todo el contenido más reciente en su correo electrónico varias veces al mes.